Tuesday
The Agent Committed It
An AI coding agent commits a valid OpenAI key into .mcp.json and is about to publish a public repro. Find every consumer, vault it, rotate, revoke, and keep the noon payouts running.
A secrets-security adventure
You just joined the security team. It's Tuesday, 9:00 AM. An AI coding assistant leaked a company password to GitHub, and 4,000 loans go out at noon. Fix it without breaking anything.
▶ Click here to playFree. Runs in your browser. No account, nothing to install. New to this kind of game? Pick Training first.
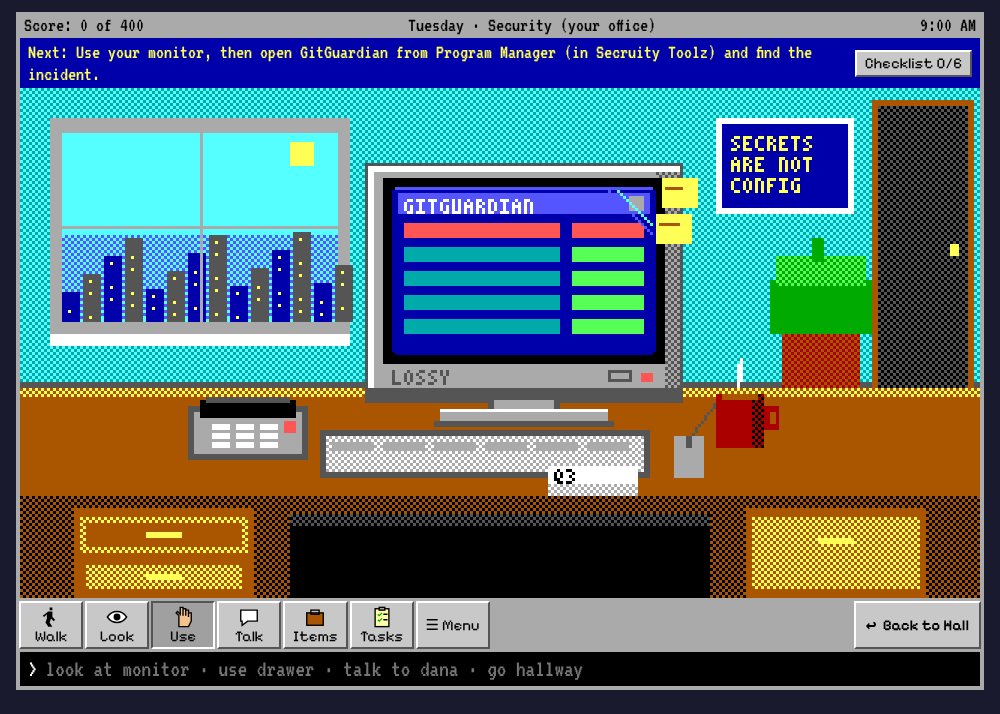
Programs use secrets, like API keys and tokens, to log in to other services. When one leaks, anyone who finds it can act as your company. Finding the leak is the easy part. Fixing it without breaking everything that uses the key is the hard part.
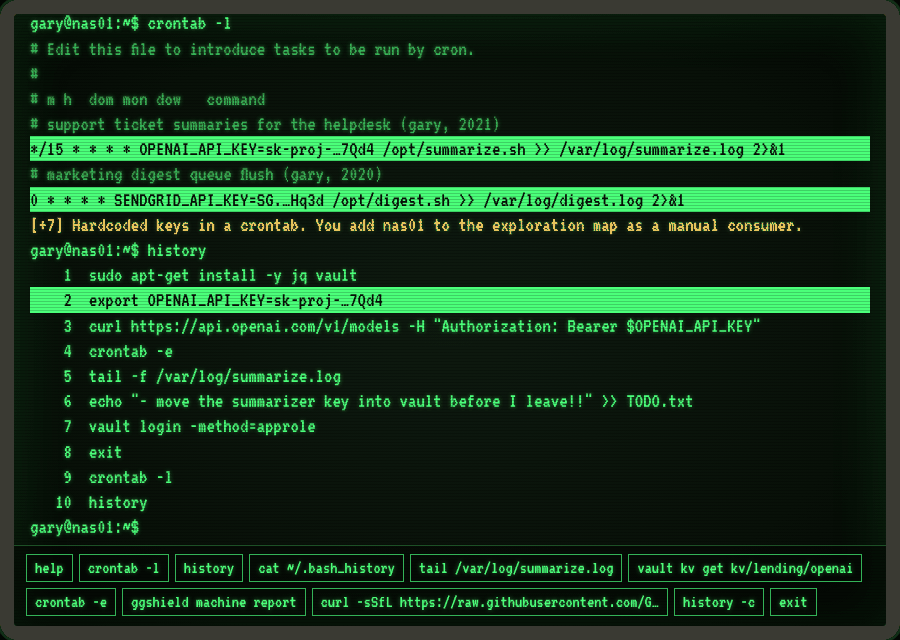
This game is about that part. You get simulated versions of the real tools: GitGuardian, a vault, CI, provider consoles and a couple of old servers. Then you work four incidents, one a day.
It plays like a 1990s Sierra adventure. Skip a step and you "die", and the game tells you which step you skipped. Then you restore and try again. Real incidents work the same way: revoke too early and payments fail, too late and a stranger spends your money.
Everything is simulated. The game is one web page. It doesn't contact any real system, and every command you type is scripted. The company and its people are made up.
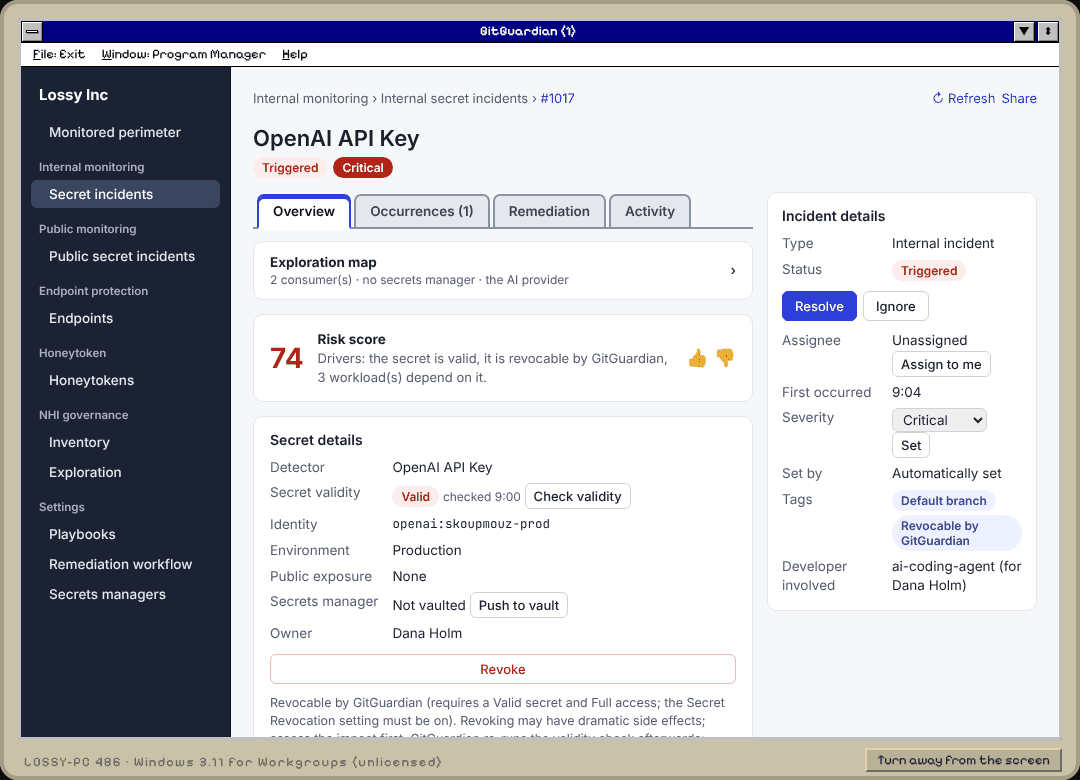
Pick a verb, then click something in the room. Or type it: look monitor, talk ravi, go hallway.
LR-1A2B-3C4D show at the end of every day. Type one in to pick up where you left off, on any device.An AI coding agent commits a valid OpenAI key into .mcp.json and is about to publish a public repro. Find every consumer, vault it, rotate, revoke, and keep the noon payouts running.
A poisoned npm package runs in CI and publishes a GitHub token and a SendGrid key. Stolen credentials mean contain first, revoke now, restore after.
A Google Cloud key from a company you bought turns up in a public Docker image. Nobody owns it, nobody has admin, and nobody remembers the VM that uses it.
A honeytoken fires on a developer's laptop. The damage is done. The only way to win is the incident playbook in your desk drawer, every step, in order. It ends the week, and you can also play it on its own.
12:00 PM.
The noon disbursement run asked repayments-svc for its go-ahead and got a 401 from the AI provider. Four thousand borrowers didn't get their loans today. The COO would like a word. Several, actually.
Assess before acting. repayments-svc used this key. Move consumers to the vault, put the new key there, then revoke the old one.
Turn it into a capture-the-flag for your team. Everyone plays the same game, and the best run wins. The game clock only moves when you act, so it's a fair race on any device.
Every end-of-day screen shows a save code. Players post their code with their score, and anyone can load it to check the run.
| Challenge | Goal | Best run is |
|---|---|---|
| Tuesday sprint | Fix Tuesday without dying. | Earliest in-game time |
| Perfect week | All four days, as close to 400 as you can get. | Highest score, then earliest time |
| By the book | ULTIMATE on its own, every playbook step in order. | Earliest in-game time |
| Find every death | See every death screen in one week. | Fewest restores |
This game exists because of the Sierra speedrunning community. Watching runners learn every room, every dead end and every death in the King's Quest games, then route around all of them, is what gave us the idea. Incident response works the same way: know the traps, and do the steps in the right order.
Lossy Inc isn't a speedrun game and has no leaderboard. The real runs, routes and records are at the King's Quest series on speedrun.com. Go watch them.
Put it on a projector and let the room argue over every click. The facilitator guide in the repository walks through each day, the traps, and what each death teaches, with links to GitGuardian's documentation.